Understand what a data breach notice really means by focusing on the specific data exposed and the risks you may face.
Even when a data breach notice looks official, you may still not know how serious the exposure is. Across 139 countries, Verizon’s 2025 Data Breach Investigations Report analyzed 22,052 security incidents, 12,195 of them confirmed breaches. What someone could do with your information won’t necessarily be clear from reassuring language about the company’s response. For your next decisions, rely on the specific data categories listed in the letter.
Read it like an incident record. Especially if it calls records “potentially affected,” compare its confirmed details with what remains unknown.
How to Read Notices About Data Breaches
Separate the incident date from the discovery date
Check the dates first. Separate the discovery and notification dates from the period when unauthorized access began and ended. Don’t treat a long gap as proof that wrongdoing occurred. Still, it changes how far back you should check account activity. Record the limit, rather than supplying a precise date, when the notice gives only a broad range or says the timeline is under investigation.
Identify who held the information
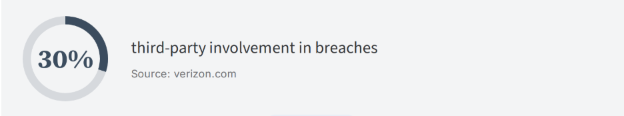
A sender you don’t recognize may be a payroll processor or medical billing company working for an organization you know. Identify both names. In Verizon’s 2025 analysis, third-party involvement doubled: a third party was involved in 30% of breaches, compared with 15% previously. Even when the notice arrives on your employer’s letterhead, determine who collected your information and whose system was affected.
Look for specifics behind the response language
Start by locating the exposed fields and affected system. While “Accessed” doesn’t necessarily mean copied, “viewed” points to inspection; “downloaded” means someone made a copy. With “Potentially affected,” involvement remains uncertain. Statements about acquisition matter, as does any mention of “exfiltration,” meaning data transferred out of a system. Also record the company’s containment steps and monitoring offer, plus the enrollment deadline and contact information.
Verify the sender through a known website or trusted phone number before submitting personal information. In follow-up phishing messages, criminals can reuse details from a real letter.
Match Your Response to the Information Exposed
What you do next should follow the category of compromised information. Compare this reference on data breaches with the notice as you weigh risks involving passwords, Social Security numbers, financial details, and medical records.
Passwords and login credentials
When passwords appear in the breach notice, change the affected one first; afterward, replace any versions you’ve reused on other accounts. Beyond the breached service, reused credentials can put other accounts at risk. In Verizon’s 2025 report, credential abuse accounted for 22% of initial access vectors. Instead of using minor variations, choose unique passwords and turn on multifactor authentication where it’s available, such as an additional sign-in code.
Financial account and payment details
Purchases charged to the card are a concern when payment-card details are exposed; bank-account details may put money held in that account at risk. Through a trusted number, call the issuer or bank to review transactions and ask about replacement credentials. You aren’t automatically required to close the account.
Social Security numbers and identity data
Your exposed Social Security number deserves serious attention. Someone can combine that persistent number with your name or birth date, then attempt impersonation or open accounts in your name. A password reset alone can’t address that exposure because, unlike a password, you normally can’t replace the number as a routine precaution. Consider freezing your credit, and continue reviewing your credit reports.
Medical and insurance records
Diagnoses or treatment details may appear in exposed medical records. Exposure can include insurance member numbers, too. In your insurer’s explanations of benefits, look for unfamiliar claims and question any provider or prescription you don’t recognize. Also check your healthcare records, because a credit freeze won’t detect misuse of your health insurance.
Choose the Protection That Fits the Risk
Compare the available protective measures
Each problem calls for a different tool. Base your choice on the exposed information.
| Protective measure | Use it when | What it does | Important limit |
| Password change | A password or login credential was exposed | Blocks continued use of the old credential | It does not protect credit files or financial account numbers |
| Account monitoring | Payment or banking information may be involved | Helps identify unfamiliar transactions | It generally detects activity after it occurs |
| Fraud alert | Identity information may be misused for credit applications | Asks prospective creditors to take identity-verification steps | It does not block access to the credit report |
| Credit freeze | A Social Security number or comparable identity data was exposed | Restricts access to the credit file until the consumer lifts the freeze | Place it with each nationwide credit bureau |
| Identity-theft report | Someone has already used your identity | Creates a recovery plan and documentation of the reported misuse | It is a response to suspected or confirmed misuse, not routine monitoring |
Decide between a fraud alert and a credit freeze
Under the Federal Trade Commission’s guidance on credit freezes and fraud alerts, a freeze is free and restricts access to your credit file. At each nationwide credit bureau, you’ll need to request it separately. A fraud alert instead asks businesses to verify your identity before opening new credit. Contact one bureau; it then informs the other two bureaus.
A freeze is especially reasonable after exposure of your Social Security number or similarly persistent identity information. For compromised login credentials, change the affected passwords immediately. When a leaked file includes your password and Social Security number, for example, that notice justifies both responses.
Preserve the Notice and Escalate Confirmed Misuse
Keep an incident file
Retain the original paperwork. Along with confirmation that you enrolled in monitoring, save the complete notice with its envelope or email headers. Call notes need dates. For disputed charges or unfamiliar credit inquiries, record dates; with rejected claims, include the provider’s name.
Use monitoring without mistaking it for prevention
When monitoring is offered, it can alert you to covered activity, but it can’t replace protective measures that fit the exposure. Find out which records it watches. Direct account reviews are still necessary, and the exposed information may also require password changes or a credit freeze. Note the enrollment deadline, then save the confirmation with your notice.
Report identity theft and consider legal guidance
If someone has used your identity, go to IdentityTheft.gov to get a recovery plan and documentation of the reported misuse. If you’ve documented financial loss or recurring fraudulent accounts, consider legal guidance as well. Advice may be warranted for tax or medical identity theft, as well as unresolved questions about your rights under applicable law. A notice alone doesn’t establish a right to compensation. Bring the incident file, including your disputed account records.
A Notice Becomes Useful When You Read the Details
The information exposed, and how long someone else can still use it, determine how serious the notice is. Urgency rises with evidence of actual misuse. Still, you needn’t wait for a fraudulent account before taking a proportionate precaution. Using a preserved record of what happened, fit your response to the specific data named in the notice.
Sources
- Verizon, 2025 Data Breach Investigations Report, April 23, 2025.
- Federal Trade Commission, What To Know About Credit Freezes and Fraud Alerts.
- The FTC identity theft recovery service provides reporting tools and a personalized recovery plan.